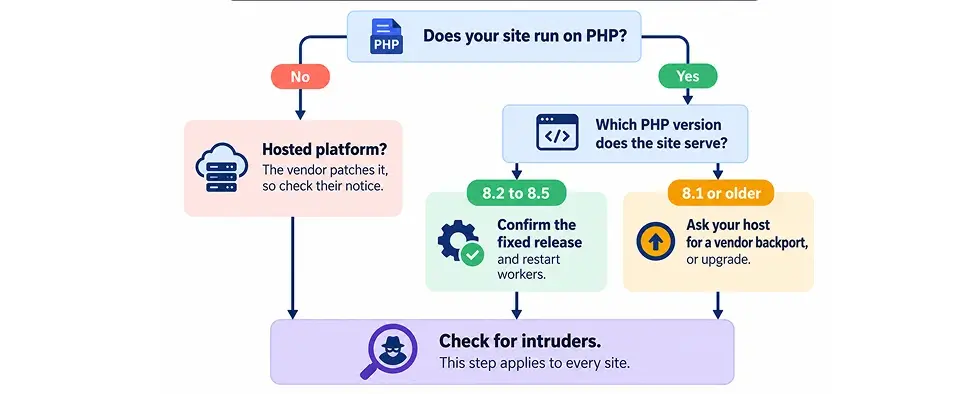
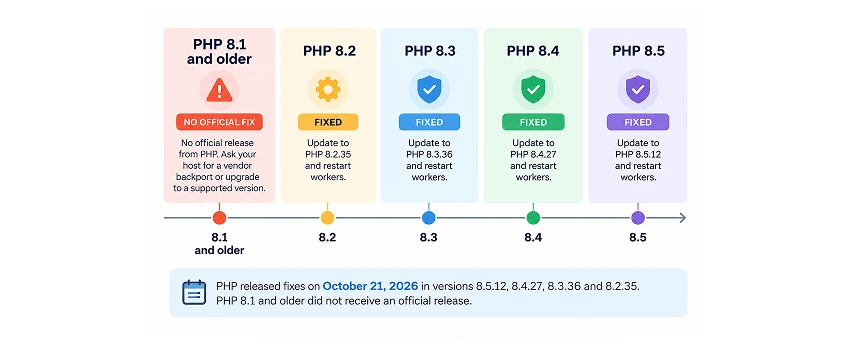
PHP2Shell is the name for two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, that let an attacker run code on a web server without logging in. It affects every site served by an unpatched PHP. PHP shipped fixes on Oct 21, 2026, in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP 8.1 and older got no official release, so those sites need a vendor backport or an upgrade.
If your website runs on PHP, you have a security job to do this week.
PHP2Shell is the PHP vulnerability 2026 owners are hearing about from hosts, developers and the news. Two flaws inside PHP itself can let a stranger run code on your web server without logging in.1 Attackers were reported probing for them before PHP shipped fixes on Oct 21, 2026.2
You do not need to read code to act. You need three answers. Is your PHP fixed? Is the fix live on the server that serves your site? Has anyone checked for a break-in? If nobody on your team owns server updates, ongoing application support is one way to close that gap.
What Is PHP2Shell? The PHP Vulnerability of 2026 in Plain Words
PHP2Shell is the nickname for two security flaws in PHP, the software behind WordPress, WooCommerce and many other sites. PHP's advisories rate each one Critical, 9.2 out of 10 on the CVSS 4.0 scale.1
The two flaws
- CVE-2026-109618: a crafted request can push PHP out of memory mid-setup, and the cleanup then works on broken data.1
- CVE-2026-109619: PHP can reuse leftover data from an earlier request, which attackers can steer into running their code.1
No login is needed. PHP confirmed an attack on Apache with mod_php using default settings, and says other setups, such as PHP-FPM, may also be affected.1
Are attackers using PHP2Shell?
Reports differ. Cloudflare and Aikido reported attacks on Oct 21, before the fixes shipped.2 Greenbone lists Amazon, watchTowr and New Zealand's NCSC as reporting exploitation.3 Canada's Cyber Centre had identified none on Oct 21 and said that could change quickly.4 CERT-EU warns that proof-of-concept code is circulating.5 Treat your site as a target.
Is Your Website Affected? A Quick Exposure Check
Your site is exposed if three things are true. It runs on PHP. That PHP is not a fixed release or a vendor-patched build. And the server answers web requests from the internet.1 That describes most WordPress, WooCommerce, Magento and custom PHP sites.
About 2.24 million internet-facing hosts show PHP, and 59% of those that reveal a version run a branch with no official fix (Shodan counts, Oct 20, 2026).2 These count servers, not websites.
Probably not your job: fully hosted platforms
Hosted store platforms such as Shopify and BigCommerce run their own servers, so patching is the vendor's job. Check their status page.
Your job: everything you host or rent
- A VPS or dedicated server that you or a developer manages
- Shared or managed hosting, where the host controls PHP
- Third-party tools and containers that bundle their own PHP5
Not sure what runs where? A technology stack assessment lists every site, plugin and server you depend on.
PHP Security Update Status by PHP Version (October 2026)
PHP supports each version for two years of regular fixes, then two more years of security fixes only.6 This table shows where each version stands as of Oct 26, 2026.
| PHP version | Security support ends | PHP2Shell fix from PHP | What to do |
|---|---|---|---|
| 8.5 | Dec 31, 2029 | 8.5.12 | Update, restart workers |
| 8.4 | Dec 31, 2028 | 8.4.27 | Update, restart workers |
| 8.3 | Dec 31, 2027 | 8.3.36 | Update, restart workers |
| 8.2 | Dec 31, 2026 | 8.2.35 | Update now, plan a move to 8.3+ |
| 8.1 | Ended Dec 31, 2025 | None (source patches only) | Vendor backport, then upgrade |
| 8.0 | Ended Nov 26, 2023 | None (source patches only) | Vendor backport, then upgrade |
| 7.4 | Ended Nov 28, 2022 | None (source patches only) | Vendor backport, then upgrade |
| 7.3 and older | 7.3 ended Dec 6, 2021 | None | Upgrade. PHP offers no fix |
Dates: php.net.67 Fixed releases: PHP's advisories.1
How to Find Your PHP Version
You can find your PHP version in five minutes:
- WordPress: Go to Tools, then Site Health, then the Info tab, and open the Server section.
- WooCommerce: Go to WooCommerce, then Status, and read the Server environment block.
- Hosting panel: cPanel's MultiPHP Manager and Plesk's PHP Settings show the version assigned to each domain.
A version number alone does not prove you are safe. Vendors patch old PHP builds without changing the number, so 8.1.34 can be fixed or not.8 Treat it as step one, not the verdict.
Why Updating WordPress or Plugins Does Not Fix PHP2Shell
WordPress, WooCommerce and plugin updates change your site's code. PHP2Shell lives one layer below, in the server's PHP. CMS and plugin updates will not apply the fix.2 PHP's advisories say updating PHP is the only complete mitigation.1
What to Ask Your Hosting Provider About PHP2Shell
Your host controls PHP on most shared and managed plans. Send these four questions today and keep the answers in writing.
| Ask your host | A good answer | A warning sign |
|---|---|---|
| Is the PHP my site uses patched for PHP2Shell? | Yes, with a package name, build date or advisory ID you can check | "We run the latest version" with no proof |
| Did you restart every PHP worker after patching? | Yes, with the restart time | "It should restart by itself" |
| My site runs PHP 7.4, 8.0 or 8.1. Do you ship a vendor backport? | Yes, naming the vendor build | "PHP no longer supports that version" |
| Have you checked my account for signs of attack? | Yes, with a log review back to Oct 17 | "Patching makes you safe" |
Running workers keep old code until they restart.2 cPanel and Plesk report fixed builds for old versions. Amazon logged attacks from Oct 17.3
How to Verify the PHP Security Update Is Live
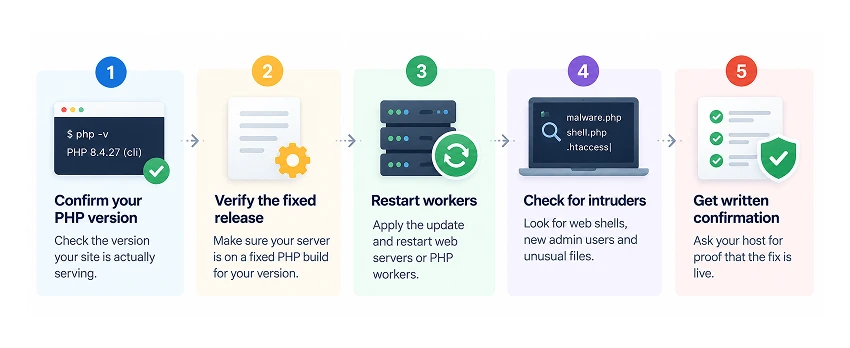
Do not take "it is patched" on trust. Run these five checks.
- Get a build ID. Ask for the exact package string or build date. Patched backports often keep the old number.8
- Check what the site serves. Test the version your site reports while serving a page, not the command line version.2
- Confirm the restart. Every PHP worker and pool must restart on the fixed build.28
- Match the advisory. Compare the build with your vendor's notice. Plesk dates its fixed builds Oct 21, 2026.8
- Retest. Load key pages, log in, submit a form and run a test checkout.
Temporary Fixes Reduce Risk, but They Do Not Patch PHP2Shell
PHP lists stopgaps, such as switching off session.upload_progress. Its advisories say they reduce risk but do not fully address the flaws.1 CERT-EU agrees they do not make an installation safe.5
A web application firewall (WAF) can lower exposure to known attack patterns, and Cloudflare extended its WAF rules to every plan, including Free.2 It is not a complete fix. Only a patched PHP removes the risk.
If your host cannot patch yet, CERT-EU and Canada's Cyber Centre advise isolating internet-facing applications from the public network until the fix is verified.45
After Patching: Check for Signs of a Break-In
Patching closes the door. It does not remove someone who is already inside.9 Attack attempts were reported from Oct 17,3 so look back that far. Check for:
- Web shells (hidden files that give an attacker remote control)
- Changed or new files in themes, plugins and core folders
- New admin users, scheduled tasks or unknown outbound connections
If you suspect a break-in, isolate the site, keep the logs, change every password and key, and rebuild from a clean backup.9 A code audit reviews the PHP code itself, so pair it with your host's log check.
Running PHP 7.4, 8.0 or 8.1? Backport Now, Upgrade Next
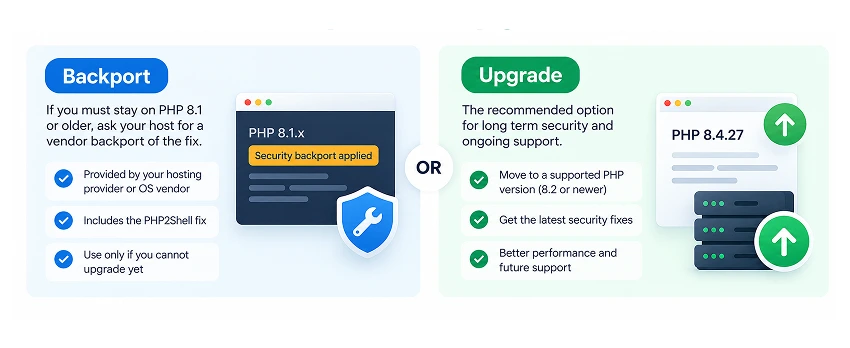
These versions got no official PHP2Shell release. PHP's security team posted source patches for people who build PHP themselves, and a hosting account cannot apply them.2
Your three options
Option 1: Get a vendor backport
Who ships them. cPanel and Plesk report fixed builds for 7.4, 8.0 and 8.1.3 Some Linux distributions and long-term-support vendors also backport fixes.9
What a backport does not cover. It closes PHP2Shell and nothing else. php.net warns that unsupported versions may expose you to flaws fixed in newer ones.7
Option 2: Restrict access
With no backport, take the site off the public internet until it is fixed.5
Option 3: Upgrade PHP
Aim for PHP 8.3 or newer: PHP 8.2 gets the fix, but its security support ends Dec 31, 2026.6 WordPress 7.0 requires PHP 7.4 or newer and recommends 8.3 or newer.10 Upgrades can break old plugins and custom code, so test on staging first. Moving off old PHP is often a legacy application modernization job.
WooCommerce and Adobe Commerce Stores: What to Test
PHP runs checkout and payments. WooCommerce recommends PHP 8.3 or newer, and WooCommerce 11.6, planned for February 2027, will require 8.1 or newer.11
Before any version change, test checkout, payments, shipping, tax, order sync and every extension. Adobe Commerce and Magento stores should also confirm their version supports the target PHP. Adobe Commerce security services cover patching and vulnerability monitoring for these stores.
If running PHP is more than your team wants, a hosted platform removes server patching from your list. See our WooCommerce to Shopify migration service, or 7 signs your ecommerce platform is holding back growth.
Frequently Asked Questions About PHP2Shell
What is PHP2Shell, the PHP vulnerability of 2026?
Two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, each scoring 9.2 out of 10. Each can let an attacker run code on a web server without logging in.1
Is my website affected by PHP2Shell?
Yes, if your site runs on PHP that is not a fixed release or a vendor-patched build. Hosted platforms patch their own servers.
Which PHP versions fix PHP2Shell?
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, released Oct 21, 2026.1 Versions 8.1 and older need a vendor backport or an upgrade.2
Is PHP 8.1 still supported?
No. PHP 8.1 reached end of life on Dec 31, 2025, and its last release was 8.1.34.7
Is PHP 8.1 outdated?
Yes, for security. PHP stopped fixing it on Dec 31, 2025, so it needs a vendor backport now and an upgrade soon.37
Is PHP 8.2 still supported?
Yes, for security fixes only, until Dec 31, 2026.6 Version 8.2.35 fixes PHP2Shell.1
What is the most recent stable version of PHP?
As of Oct 26, 2026, PHP 8.5 is the newest branch, and 8.5.12 is its fixed release.16
Does updating WordPress fix PHP2Shell?
No. The fix is in the server's PHP, and WordPress, plugin and theme updates do not apply it.2
Can a firewall stop PHP2Shell?
It can lower exposure to known attack patterns, but PHP says only updating is a complete fix.1
Your PHP2Shell Checklist
The PHP2Shell response in one line
- Patch the server, prove it with a build ID, then check for intruders.
- Last checked: Oct 26, 2026.
Not sure whether your site is patched?
Redefine reviews your PHP setup for free and sends a written upgrade outline. Send your site address to get started.
See Redefine's development support and maintenance services
Sources & Citations
All sources opened on Oct 26, 2026.
- PHP project, CVE-2026-109618 and CVE-2026-109619: primary advisories, severity, fixed versions.
- CybelAngel, What we know about PHP2Shell: older versions, exposure, attacks.
- Greenbone, PHP2Shell remote code execution: exploitation, cPanel and Plesk.
- Canadian Centre for Cyber Security, Alert AL26-026: exploitation status, isolation.
- CERT-EU, Security Advisory 2026-018: mitigations, unsupported PHP.
- PHP, Supported Versions: support policy and dates.
- PHP, Unsupported Branches: end-of-life dates.
- Digital Applied, PHP2Shell fixes by distro, control panel and PHP version: backports, build checks.
- ThreatLocker, PHP2Shell: Why Organizations Must Patch: post-patch checks, vendor backports.
- Make WordPress Core, Dropping support for PHP 7.2 and 7.3: WordPress 7.0 PHP versions.
- WooCommerce Developer Blog, New requirement for WooCommerce 11.6: PHP requirement.
Change log: Oct 26, 2026, first version. Recheck daily while PHP2Shell is active and after every PHP security release. Refresh by Jan 1, 2027, when PHP 8.2 security support ends.
Umang Patel
Co-owner | Ecommerce Architecture, Systems & Integrations
Umang Patel has worked in ecommerce and technology since 2001. He specializes in backend systems, ecommerce architecture, ERP and platform integrations, automation, and reverse engineering complex business processes. At Redefine Innovations, he leads technolo
Areas of expertise: Ecommerce Architecture • Backend Systems • ERP Integration • Automation • Headless Commerce • Reverse Engineering